
OT Connectivity is Inevitable; Ownership is a Choice
I recently switched to T-Mobile home internet (this isn't a plug; the jury is still out on customer satisfaction). But the speed to connection was incredible: I pulled the modem out of the box, plugged it into the wall, scanned a QR code, and I was immediately up and running.
This capability level is true for just about any device installed in commercial buildings as well. Plug it in, and it's ready to connect to... whatever it's allowed to connect to.
When you're an OT network professional, the marvel of my T-Mobile "plug it in and you're connected" story becomes much more of a nightmare.
In our first NexusCast on Device Management, Peter O'Connor, IT Director at Inova Health Systems, shared what that nightmare looks like. The Department of Homeland Security called Inova to say that they had found a rogue cellular connection tied to an Inova address. After two weeks of hunting down the device, they found a water treatment system broadcasting on its own to a cellular network, unbeknownst to O'Connor's team.
The connectivity of your buildings is entirely inevitable. What isn't inevitable is whether anyone takes ownership of those connections.
Below, we discuss the levels of OT network ownership we see within our community: from no ownership, to the messy middle of vendor/owner gray areas, to corporate IT ownership. We'll end with the NexusCon sessions built for each level.
The starting point: no ownership
When we asked a room of building owners how painful device management is at their buildings today, nearly two-thirds scored themselves a 6 or higher out of 10. The service providers in the room were even less confident: they put their clients' average at a 9.
That pain doesn't come from anyone deciding "no ownership." It comes from nobody ever sitting down to decide ownership.
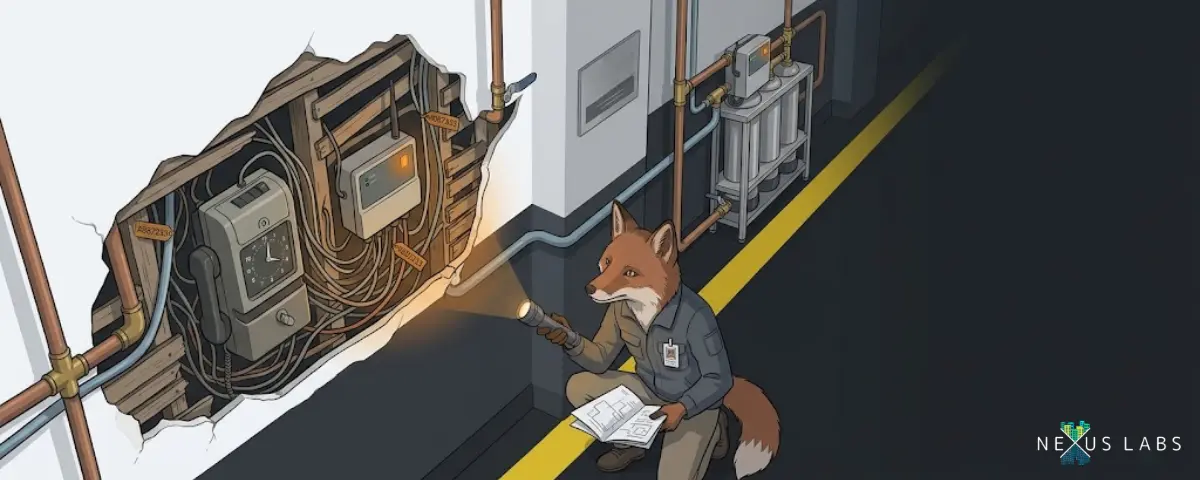
The obvious risk of no ownership is the growing cyberattack vulnerability of OT systems (which we'll cover in depth in our Under Siege NexusCon session). If that's not reason enough, no ownership also has a quieter operational cost. At the NexusCast, John DeVeaux, Enterprise Architect at Hines, told the story of an assessment walk-through where his team traced a mystery line into a wall, tore open the sheetrock, and found the building's original time clock, still wired to a phone line somebody had been paying for twenty years. Nobody had dared disconnect what nobody understood.
The same accumulation happens in your server room. Without ownership rules, every new system arrives with its own connection and its own hardware, and you end up with racks of redundant components all doing the same job. At NexusCon's BAS Reboot session, Altura will show how containerizing BAS instances cuts the cost of onboarding new systems, and it all starts with ownership of devices.
The messy middle: vendor/owner gray areas
When an owner starts questioning the devices vendors bring into their buildings, the default solution has been the air gap. An 'air gap' puts each OT system on its own, entirely isolated network: none of the complexity or risk of integrating with the building's base network. But it isn't the panacea. Two issues keep coming up with these isolated networks:
- An isolated network is only as isolated as its configuration. Attackers recently shut down a Polish heating plant serving 50,000 residents. A private, isolated cellular network connected to a wind farm was reconfigured by the hacker, giving them control of the heating plant. Colin Jenkel, Smart Buildings Systems Development Manager at Amazon, who shared the story with us, said, "I can't tell you the number of times I have heard from vendors, 'Don't worry, we have our own cell endpoint to configure our systems' - not once have I trusted that answer, and no one else should either."
- Isolated networks owned by your vendor remove your visibility to the path. Inova's water treatment system took weeks to find for one reason: they never owned the connection. If you give all control to your vendors, you're at the mercy of their diligence for vulnerability and uptime. Inova requires all connectivity to be on their own network because they "can't afford a disruption from an 'isolated' or air-gapped network being compromised".
The messy middle gets even messier depending on the building's ownership model. We spoke with the OT manager for a massive tech company that acts as a tenant in the majority of its buildings across 30 countries. The landlord's network is the landlord's, so his team's ownable footprint is small. So, they shrink what they own and defend, and make their vendors own the rest. For a recent cloud BMS deployment, the vendor hosts, manages, and patches the environment. The OT manager's team guards one thing: the link between the vendor's cloud and their own equipment. "If I see any issues, I'm going to cut things right away."
Finally, we're hearing a growing tension between integrated facilities management teams, like CBRE, JLL, and Cushman & Wakefield, and the major corporations they support. These teams are experts at deploying and operating building technology, but they seldom carry dedicated networking specialists. So when a corporation pushes OT network ownership down to its FM partner, the FM team has to stand up a specialty it was never staffed for. When the corporation holds ownership instead, the FM team and every vendor underneath it have to learn to abide by the owner's IT department's strict rules.
Good but never complete: enterprise IT ownership
At the top of the deliberateness ladder is full enterprise IT ownership: one converged network, run by the building owner's IT, with facilities devices treated like any other endpoint. In our device management pain poll, the lowest scores in the room all came from this group. But don't assume this level equals completion. JPMorgan Chase built a brand-new headquarters, ran a full device discovery program on a network their IT team controlled, and still found cameras, access points, and VoIP phones on the OT network that were never supposed to be there. Ownership at this level doesn't mean surprises stop; it means you find them quicker. And it only works when the IT/OT relationship is real.
Evolving from one level to the next
Wherever you sit today, there's a NexusCon session built to help you evolve to the next level:
For those with no ownership: One Asset, One Identity covers how OT and FM teams make sure every device in the building is known, tracked, and integrated. Policing the Chatter explains how to turn your network's health from a gut feeling into a number your leadership can see and fund.
For those in the messy middle, Under Siege shows how owners run vulnerability response with their vendors as a normal operating rhythm.
And if you're pushing towards enterprise IT ownership, nobody gets there without a strong IT/OT relationship underneath it. Our Building Owner Kickoff (exclusive to building owners) will talk through the moves mature owners have used to build that relationship.
See you there!
Sign up for the newsletter to get 5 stories like this per week:
I recently switched to T-Mobile home internet (this isn't a plug; the jury is still out on customer satisfaction). But the speed to connection was incredible: I pulled the modem out of the box, plugged it into the wall, scanned a QR code, and I was immediately up and running.
This capability level is true for just about any device installed in commercial buildings as well. Plug it in, and it's ready to connect to... whatever it's allowed to connect to.
When you're an OT network professional, the marvel of my T-Mobile "plug it in and you're connected" story becomes much more of a nightmare.
In our first NexusCast on Device Management, Peter O'Connor, IT Director at Inova Health Systems, shared what that nightmare looks like. The Department of Homeland Security called Inova to say that they had found a rogue cellular connection tied to an Inova address. After two weeks of hunting down the device, they found a water treatment system broadcasting on its own to a cellular network, unbeknownst to O'Connor's team.
The connectivity of your buildings is entirely inevitable. What isn't inevitable is whether anyone takes ownership of those connections.
Below, we discuss the levels of OT network ownership we see within our community: from no ownership, to the messy middle of vendor/owner gray areas, to corporate IT ownership. We'll end with the NexusCon sessions built for each level.
The starting point: no ownership
When we asked a room of building owners how painful device management is at their buildings today, nearly two-thirds scored themselves a 6 or higher out of 10. The service providers in the room were even less confident: they put their clients' average at a 9.
That pain doesn't come from anyone deciding "no ownership." It comes from nobody ever sitting down to decide ownership.
The obvious risk of no ownership is the growing cyberattack vulnerability of OT systems (which we'll cover in depth in our Under Siege NexusCon session). If that's not reason enough, no ownership also has a quieter operational cost. At the NexusCast, John DeVeaux, Enterprise Architect at Hines, told the story of an assessment walk-through where his team traced a mystery line into a wall, tore open the sheetrock, and found the building's original time clock, still wired to a phone line somebody had been paying for twenty years. Nobody had dared disconnect what nobody understood.
The same accumulation happens in your server room. Without ownership rules, every new system arrives with its own connection and its own hardware, and you end up with racks of redundant components all doing the same job. At NexusCon's BAS Reboot session, Altura will show how containerizing BAS instances cuts the cost of onboarding new systems, and it all starts with ownership of devices.
The messy middle: vendor/owner gray areas
When an owner starts questioning the devices vendors bring into their buildings, the default solution has been the air gap. An 'air gap' puts each OT system on its own, entirely isolated network: none of the complexity or risk of integrating with the building's base network. But it isn't the panacea. Two issues keep coming up with these isolated networks:
- An isolated network is only as isolated as its configuration. Attackers recently shut down a Polish heating plant serving 50,000 residents. A private, isolated cellular network connected to a wind farm was reconfigured by the hacker, giving them control of the heating plant. Colin Jenkel, Smart Buildings Systems Development Manager at Amazon, who shared the story with us, said, "I can't tell you the number of times I have heard from vendors, 'Don't worry, we have our own cell endpoint to configure our systems' - not once have I trusted that answer, and no one else should either."
- Isolated networks owned by your vendor remove your visibility to the path. Inova's water treatment system took weeks to find for one reason: they never owned the connection. If you give all control to your vendors, you're at the mercy of their diligence for vulnerability and uptime. Inova requires all connectivity to be on their own network because they "can't afford a disruption from an 'isolated' or air-gapped network being compromised".
The messy middle gets even messier depending on the building's ownership model. We spoke with the OT manager for a massive tech company that acts as a tenant in the majority of its buildings across 30 countries. The landlord's network is the landlord's, so his team's ownable footprint is small. So, they shrink what they own and defend, and make their vendors own the rest. For a recent cloud BMS deployment, the vendor hosts, manages, and patches the environment. The OT manager's team guards one thing: the link between the vendor's cloud and their own equipment. "If I see any issues, I'm going to cut things right away."
Finally, we're hearing a growing tension between integrated facilities management teams, like CBRE, JLL, and Cushman & Wakefield, and the major corporations they support. These teams are experts at deploying and operating building technology, but they seldom carry dedicated networking specialists. So when a corporation pushes OT network ownership down to its FM partner, the FM team has to stand up a specialty it was never staffed for. When the corporation holds ownership instead, the FM team and every vendor underneath it have to learn to abide by the owner's IT department's strict rules.
Good but never complete: enterprise IT ownership
At the top of the deliberateness ladder is full enterprise IT ownership: one converged network, run by the building owner's IT, with facilities devices treated like any other endpoint. In our device management pain poll, the lowest scores in the room all came from this group. But don't assume this level equals completion. JPMorgan Chase built a brand-new headquarters, ran a full device discovery program on a network their IT team controlled, and still found cameras, access points, and VoIP phones on the OT network that were never supposed to be there. Ownership at this level doesn't mean surprises stop; it means you find them quicker. And it only works when the IT/OT relationship is real.
Evolving from one level to the next
Wherever you sit today, there's a NexusCon session built to help you evolve to the next level:
For those with no ownership: One Asset, One Identity covers how OT and FM teams make sure every device in the building is known, tracked, and integrated. Policing the Chatter explains how to turn your network's health from a gut feeling into a number your leadership can see and fund.
For those in the messy middle, Under Siege shows how owners run vulnerability response with their vendors as a normal operating rhythm.
And if you're pushing towards enterprise IT ownership, nobody gets there without a strong IT/OT relationship underneath it. Our Building Owner Kickoff (exclusive to building owners) will talk through the moves mature owners have used to build that relationship.
See you there!
Sign up for the newsletter to get 5 stories like this per week:


This is a great piece!
I agree.